
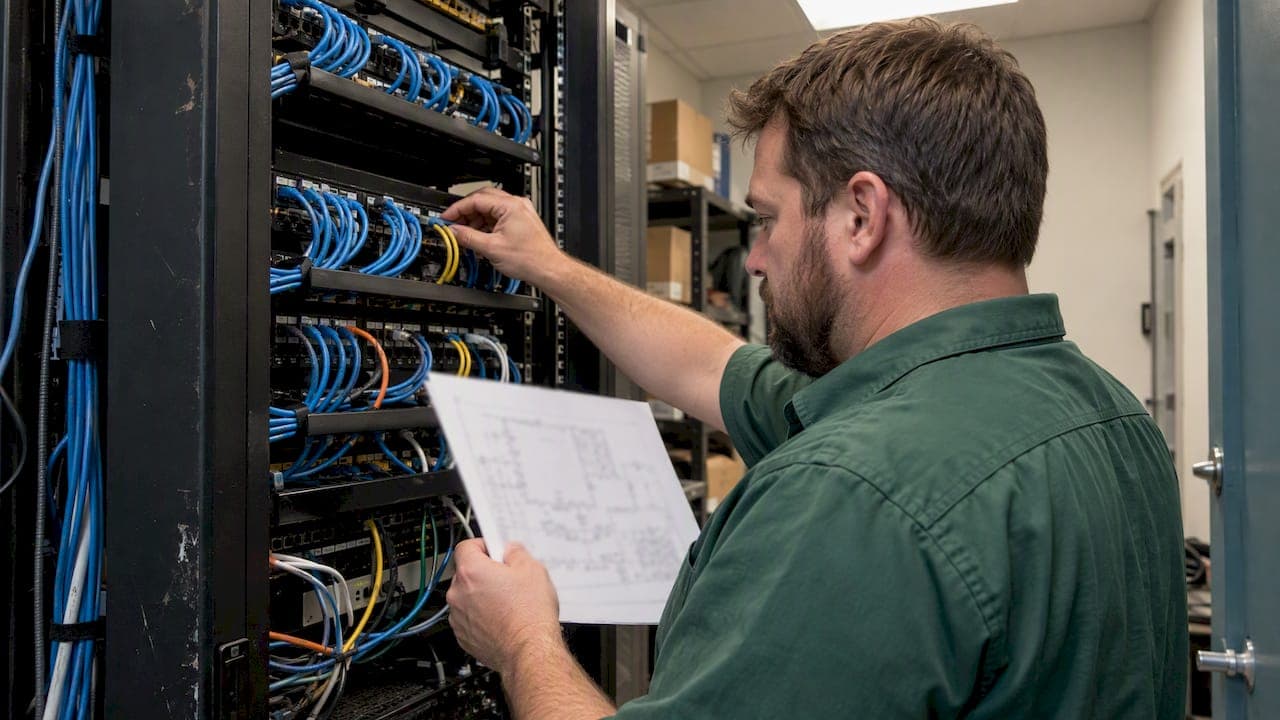
A standards-aligned network documentation set needs four components: Layer 1/2 and Layer 3 diagrams, a complete asset inventory with an IP allocation table, patch and change logs, and a documented review cadence tied to a configuration baseline. Each of these maps directly to CIS Control 1, CIS Control 4, and NIST SP 800-128. Larger or faster-changing networks need automation and a single Source of Truth to keep all four current.
TL;DR:
- Regularly review asset inventory, network diagrams, and change logs at least annually to ensure accuracy and maintain compliance with standards.
- Automate inventory updates using discovery tools and passive methods to avoid outdated data and reduce manual effort.
- Maintain clear ownership, change control workflows, and version control for all documentation to ensure audit readiness and traceability.
- Add specialized diagrams like Wi-Fi heatmaps, security segmentation, or cloud architecture when network complexity exceeds small or mid-sized environments.
- Follow prescribed review frequencies, such as bi-annual asset reviews and annual configuration updates, aligned with CIS, ISO, and NIST standards.
- ✓Comprehensive cybersecurity
- ✓Rapid data recovery
- ✓Customized IT plans
Table of Contents
- The documentation you must have and the fields each record needs
- Diagrams worth adding when Wi-Fi, security, or cloud complexity grows
- What CIS, ISO/IEC 27002, and NIST require, and how often to review
- Keeping documentation accurate: ownership, change control, and audit readiness
- Tools and formats that make documentation usable, not just stored
- How managed IT turns these standards into daily practice
- Get your network documentation audit-ready without the extra workload
- FAQ
- Sources
The documentation you must have and the fields each record needs
Every network, regardless of size, needs a baseline set of records that an auditor, a new technician, or an incident responder could pick up cold and use to understand what exists and how it connects.
Layer 1 and Layer 2 documentation covers the physical and switching layer: rack elevations, port-to-port mappings, patch panel layouts, and a consistent labeling convention for cables and ports. Without this, a technician tracing a bad link has to physically follow cable runs instead of reading a diagram.
Layer 3 documentation covers the logical layer: subnet ranges, VLAN assignments, routing adjacencies between devices, and an index pointing to where firewall rule sets live. This is the layer most audits actually ask about, because it shows how traffic is supposed to move and where it is supposed to be blocked.
The asset inventory is the record that CISA guidance treats as the answer to "what is on the network?" It needs hostname, MAC address, serial number, assigned owner, department, physical location, device role, firmware or OS version, and support contract status for every device.
An IP allocation table sits alongside it, recording each subnet's CIDR block, its purpose, the owning team, whether addresses are static or DHCP-assigned, and any reservation notes. A circuit table rounds out the connectivity picture: carrier name, circuit ID, provider contact, bandwidth, and SLA terms, which matters when a connectivity problem needs an escalation call at 2 a.m.
- Patch and firmware table: device name, current version, available version, scheduled patch date, and verification status.
- Change log: date, change description, requestor, approver, pre-change and post-change snapshot references.
- Example change log row: "2026-03-14, firewall rule update for new VPN subnet, requested by network admin, approved by IT manager, config backup ID attached."
| Document | Core fields |
|---|---|
| Asset inventory | Hostname, MAC, serial, owner, department, location, role, firmware/OS |
| IP allocation table | CIDR, purpose, owner, DHCP/static, reservation notes |
| Circuit table | Carrier, circuit ID, provider contact, bandwidth, SLA |
| Patch/firmware table | Device, current version, available version, patch date, verification status |
A patch management policy template can shorten the time it takes to stand up the patch table and tie it to a recurring schedule instead of an ad hoc one.
Diagrams worth adding when Wi-Fi, security, or cloud complexity grows
Not every network needs every diagram type. The core four documents cover most small and mid-sized environments, but certain conditions justify adding more detail.
Wi-Fi heatmaps earn their place once a building has more than a handful of access points or recurring coverage complaints. The minimum useful record includes AP ID, channel assignment, transmit power, and antenna orientation, since that is what a technician needs to diagnose a dead zone without re-walking the whole floor.

Security diagrams matter once segmentation gets complex enough that a single firewall rule list cannot describe it visually. A high-level segmentation diagram should show network access control (NAC) boundaries and intrusion detection or prevention (IDS/IPS) placement, while the granular firewall rule sets stay in their own referenced document rather than cluttering the diagram.
Cloud architecture diagrams become necessary once virtual private cloud (VPC) resources, peering connections, or VPN links start multiplying. These should map subnet structure, peering and VPN relationships, and access control boundaries, since cloud sprawl is harder to track by memory than an on-premises rack.
- Routing protocol or BGP diagrams: needed once more than one autonomous system or complex adjacency exists; record peer relationships and route policies.
- Cable plans: useful for large or multi-floor sites; record conduit paths and cable types alongside the Layer 1 diagram.
- Smaller networks: merge diagrams into one combined physical/logical view to avoid maintaining documents nobody updates.
- Large or distributed networks: split diagrams by site or function so each owner can update their piece without touching the rest.
What CIS, ISO/IEC 27002, and NIST require, and how often to review
Standards bodies do not just recommend documentation. They specify what it must contain and how often it must be reviewed, which is the detail most internal documentation efforts miss.
CIS Control 1 requires an accurate enterprise asset inventory containing network address, MAC address, owner, and department for every asset, reviewed at least bi-annually, with active discovery tools recommended to keep it current rather than relying on manual updates. CIS Control 4 requires a secure configuration process for network infrastructure, with documentation reviewed or updated annually or whenever a significant change occurs. CIS guidance also calls for architecture diagrams to be established and reviewed on a similar annual cycle, treating them as required artifacts rather than optional extras.

ISO/IEC 27002 frames configuration management around ensuring that hardware, software, and networks maintain their required security settings and preventing unauthorized changes. The standard's configuration management pillars, planning, identification, control, status accounting, and audit, each depend on documentation existing and being current; without it, the audit pillar in particular has nothing to check against. One guide to the updated 2022 version of ISO/IEC 27002 notes that configuration management depends on a comprehensive understanding of the IT environment, which is exactly what good documentation provides.
NIST SP 800-128 describes security-focused configuration management (SecCM) in four phases: planning, identifying and implementing configurations, controlling changes, and monitoring. Documentation plays a distinct role in each phase, from defining the baseline in planning to proving compliance in monitoring.
| Document | Control(s) satisfied | Evidence to keep |
|---|---|---|
| Asset inventory | CIS Control 1 | Dated export, review log |
| Secure config process | CIS Control 4 | Annual review sign-off |
| Architecture diagrams | CIS Control 1 (background) | Version history, review date |
| Change log | NIST SP 800-128 (control phase) | Approval chain, timestamps |
- Review the asset inventory regularly as recommended by CIS Control 1 guidance.
- Review configuration documentation and diagrams regularly, including after significant changes, per CIS Control 4 guidance.
- Tie every documentation review to a SecCM phase so monitoring evidence maps back to a planning decision.
Keeping documentation accurate: ownership, change control, and audit readiness
Documentation decays the moment nobody owns it. Every artifact needs a named steward responsible for keeping it current and a publishing rule that says where the current version lives and who can edit it.
- Assign an owner per document. The person who manages firewalls owns the firewall rule index; the person who manages switching owns the Layer 1/2 diagrams.
- Run changes through a change control workflow. A request gets submitted, reviewed, and approved before work starts; a pre-change snapshot is captured; the change deploys; a post-change snapshot confirms the result; the documentation updates before the ticket closes.
- Store documentation in version-controlled systems. A CMDB or a network source of truth (NSoT) paired with access controls and a defined retention period keeps history intact and keeps edits attributable.
- Automate inventory updates where possible. DHCP logs, passive discovery tools, and scheduled scans catch devices that show up between manual reviews, which matters because CISA guidance specifically recommends moving past spreadsheet-only inventories toward integrated, automated asset management.
- Document approved exceptions explicitly. A deviation from the standard baseline, if genuinely necessary, gets recorded with a reason, an approver, and a scheduled date for risk review, rather than being left to quietly become an unmonitored gap.
- Keep an audit readiness checklist. Current diagrams, the latest inventory export, the last two change log entries, and the most recent review sign-off should all be retrievable in minutes, not days.
Pro Tip: Fingerprint your evidence by exporting a dated, read-only snapshot of each document before every scheduled review, so auditors can see exactly what existed at a given point in time.
A CMMC self-assessment approach walks through documenting baseline deviations and approved exceptions in more detail, which is worth a look for anyone preparing for a compliance review rather than a routine internal audit.
Tools and formats that make documentation usable, not just stored
The right tool choice depends less on brand preference and more on whether the output needs to be shared quickly or archived reliably.
Diagram tools like Visio or diagrams.net work for both purposes, but the export format should change with the use case: SVG or PNG for quick sharing in a ticket or chat, native Visio XML when the diagram needs to stay editable for the next person who touches it.
A CMDB or network source of truth should be built around a small set of core fields and a unique identifier per asset, exposed through an API so other tools, such as discovery scanners or ticketing systems, can read and write to it without manual re-entry. Discovery itself should combine active scanning with passive methods: DHCP logs, SNMP polling, and log aggregation, run on a defined schedule rather than only when someone remembers.
- Export inventories as CSV or JSON so other systems can ingest them without reformatting.
- Use OSCAL or a similar machine-readable format for security plans where a formal compliance package is required, per NIST's OSCAL reference.
- Redact sensitive fields such as credentials or private keys before sharing any export outside the core team.
- Publish documentation through an internal wiki so updates propagate without re-emailing files, an approach covered in this guide to broadcasting documentation via Confluence.
| Pattern | What it connects |
|---|---|
| Discovery to inventory | Scanners and DHCP logs feed the authoritative asset list |
| Inventory to diagrams | Current inventory data drives diagram generation |
| Diagrams to audit export | Versioned diagrams export as evidence packages |
How managed IT turns these standards into daily practice
We build documentation maintenance into Managed IT Support and Network Management rather than treating it as a one-time project. Continuous monitoring feeds inventory rollups and patch tables automatically, helping keep the asset list and firmware status current.
This continuous feed shortens mean time to repair because a technician troubleshooting an outage can pull a current diagram and change log instead of reconstructing the network from memory, and it keeps documentation ready for industry-specific compliance reviews.
— Nicholas
Get your network documentation audit-ready without the extra workload
We handle the documentation upkeep most small businesses never have time for: current diagrams, a live asset inventory, and change logs that stay accurate because our Network Management and 24/7 monitoring keep feeding them.
- Request a Free Network Assessment to see where your current documentation stands.
- Book a 10-minute readiness audit for a fast check against standards expectations.
- Talk to us about Managed IT Support for ongoing documentation and compliance upkeep across Norman, Moore, and Oklahoma City.
FAQ
What is the 5-4-3 rule in Ethernet?
The 5-4-3 rule is an older Ethernet design guideline limiting a network segment to five segments, connected by four repeaters, with only three of those segments populated by active devices. It applied mainly to legacy coaxial and early Ethernet designs and has little relevance to modern switched networks, though it still appears in some network documentation glossaries.
What are the four main types of documentation?
Most standards-aligned network documentation sets fall into four categories: physical and logical diagrams, asset inventories, configuration and change records, and policy or compliance documentation. Each category maps to specific controls, such as CIS Control 1 for inventories and NIST SP 800-128 for configuration control.
What are some examples of network documentation?
Common examples include rack elevation diagrams, Layer 3 logical diagrams showing subnets and VLANs, IP allocation tables, patch and firmware tables, and change logs recording configuration history. Larger environments often add Wi-Fi heatmaps, security segmentation diagrams, and cloud architecture diagrams as complexity grows.
Sources
- CIS Control 1: Inventory and Control of Enterprise Assets
- Guide for Security-Focused Configuration Management of Information Systems (NIST SP 800-128)
- Foundations for OT cybersecurity: asset inventory guidance — CISA