
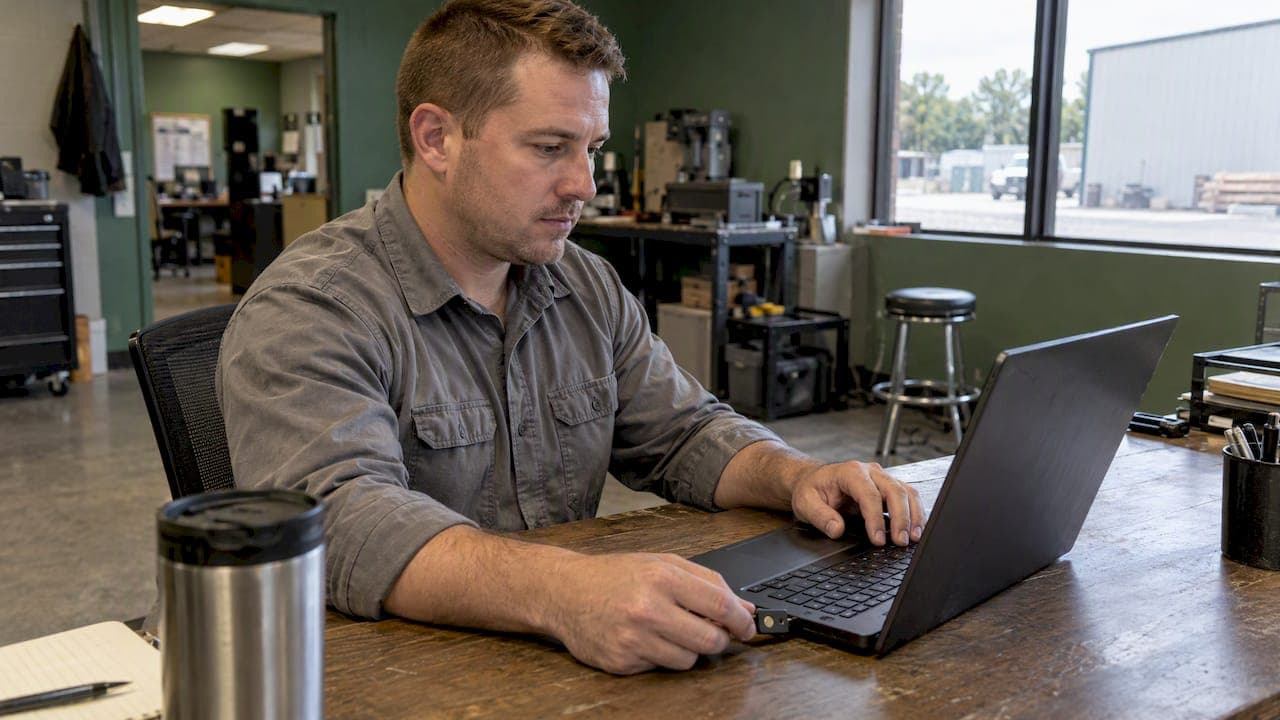
Phishing-resistant MFA is multi-factor authentication that cannot be tricked into handing a login to a fake website. It works by using a cryptographic key tied to the real site, so there is no code or approval for an attacker to capture. According to CISA, FIDO/WebAuthn is the only widely available phishing-resistant authentication today, with PKI-based smart cards as a less common option. For a small business on Microsoft 365, that means passkeys, FIDO2 security keys, or Windows Hello for Business, starting with your administrators.
Key Takeaways
- Text-message codes, authenticator-app codes and push approvals are better than a password alone, but all can be phished. Passkeys, FIDO2 security keys, Windows Hello for Business and smart cards resist phishing.
- "Passwordless" and "phishing-resistant" overlap but are not the same. Some passwordless methods still fall short of the phishing-resistant standard.
- Microsoft Entra ID, the sign-in system behind Microsoft 365, supports passkeys in Microsoft Authenticator, FIDO2 keys, Windows Hello for Business and certificate-based authentication.
- Start with administrators and anyone who touches sensitive data, then expand. Plan recovery before you enforce anything.
- Phishing-resistant MFA does not cover everything. Malware on a device can still steal session tokens, so pair it with endpoint protection.
Table of Contents
- What phishing-resistant MFA actually means
- Which methods are phishing-resistant and which are not
- Passwordless vs. phishing-resistant: the difference
- Does Microsoft 365 support phishing-resistant MFA?
- Who to protect first
- A rollout plan for a small business
- What phishing-resistant MFA does not cover
- How we help Oklahoma small businesses get there
- Common rollout mistakes
- FAQ
- Sources
What phishing-resistant MFA actually means
Standard MFA asks for a second proof after the password: a texted code, a number from an app, a push notification to approve. The weakness is that the user types or approves these things themselves. If a convincing fake login page relays what the user enters to the real site in real time, the attacker gets in and the user never knows.
Phishing-resistant methods remove that human step. The authenticator holds a cryptographic key pair bound to the legitimate website's domain. IBM explains that if a site is spoofed, the authenticator stays silent, so there is nothing for the attacker to capture or replay. The user cannot be talked into giving up something that is never shown to them.
You will also see the older phrase "verifier impersonation resistance." NIST's digital identity guidance used that term in SP 800-63-3 and planned to adopt "phishing resistance" in the next revision. Same idea, plainer name.
The federal government already treats this as the baseline. OMB memo M-22-09 requires federal agencies to use phishing-resistant methods to access agency resources. That does not bind a private dental practice, but it shows where the standard is heading, and many insurers, contractors and compliance frameworks follow federal guidance.

Which methods are phishing-resistant and which are not
CISA's fact sheet sorts the common options clearly. Here is how they line up for a small business.
| Method | Phishing-resistant? | Why |
|---|---|---|
| SMS or voice code | No | Codes can be intercepted, socially engineered or relayed to a fake site |
| Authenticator app code (OTP) | No | The user types the code into whatever page asks for it |
| Push approval | No | Users can be flooded with prompts or tricked into approving |
| Passkey (FIDO/WebAuthn) | Yes | Key is bound to the real domain |
| FIDO2 security key | Yes | Same protocol, in a physical device |
| Smart card (PIV, CAC) or other PKI-based MFA | Yes | Certificate-based, bound to the sign-in |
The classification comes from CISA's guidance on implementing phishing-resistant MFA, which calls app-based OTP, push, and SMS or voice MFA vulnerable to phishing or related attacks.
Push approvals deserve a note of their own. Attackers who already have a password can trigger prompt after prompt until someone taps Approve. We cover the warning signs in our guide to stopping MFA fatigue attacks. Moving to a phishing-resistant method closes this door instead of just watching it.
Passwordless vs. phishing-resistant: the difference
These terms get used interchangeably, and they should not be. Passwordless means you sign in without typing a password. Phishing-resistant means the method cannot be relayed or replayed through a fake site. Many methods are both, but not all.
Microsoft makes the distinction concrete with its built-in authentication strengths for Conditional Access. There are three: Multifactor authentication, Passwordless MFA, and Phishing-resistant MFA. Per Microsoft's table, the phishing-resistant strength allows Windows Hello for Business or platform credentials, FIDO2 security keys and certificate-based authentication (multifactor). The passwordless strength also allows Microsoft Authenticator phone sign-in, which the phishing-resistant strength does not. A Temporary Access Pass counts only toward the general MFA strength.
The practical reading: if your policy says "passwordless," a user may still sign in with a method that can be phished. If it says "phishing-resistant," only the stronger set gets through. For administrators and sensitive apps, choose the second.

Does Microsoft 365 support phishing-resistant MFA?
Yes. If your business runs Microsoft 365, you already have the identity platform for it. Microsoft Entra ID lists these phishing-resistant methods: passkeys in Microsoft Authenticator, FIDO2 security keys, Windows Hello for Business, and certificate-based authentication.
Is Microsoft Authenticator phishing-resistant?
It depends on the mode. Authenticator's passkey feature qualifies. Entra lists passkeys in Microsoft Authenticator as phishing-resistant. A numeric code from the app, or a push approval, does not qualify under CISA's classification. When someone says "we use Authenticator," ask which of those they mean.
What you need to turn it on
An Authentication Policy Administrator can enable passkey sign-in in the Passkey (FIDO2) policy and target specific users or groups in the Microsoft Entra admin center. Targeting a pilot group first is the safe way to do it.
Then you can use Conditional Access to require an authentication strength, such as a passkey in Authenticator. Microsoft warns that an All resources policy can create a registration loop, where users cannot register the passkey because the policy blocks the very sign-in needed to register it. Microsoft's community guidance on this problem suggests avoiding Conditional Access requirements on the Add security info registration flow, and using a Temporary Access Pass to help users register. The same thread lists Android 14 or later and iOS 17 or later as the phone requirements for passkeys in Authenticator, so check your staff's devices before you announce a date.
If you have not turned on MFA at all
Do that first. Basic MFA through Security Defaults is a fast, free first layer, and our walkthrough on starting MFA for Microsoft 365 with Security Defaults shows how. Phishing-resistant MFA is the upgrade, not a reason to wait.
Who to protect first
You do not have to convert every account in a week. NIST's small business guidance says to prioritize phishing-resistant authenticators for applications that protect sensitive information and for users with elevated privileges, and to inventory your systems to see which ones support MFA at all.
For a typical Oklahoma City office, the order looks like this:
- Global and other administrators. One compromised admin account can change every other account's settings, disable backups or exfiltrate mail.
- Finance and billing staff. Wire fraud and payroll redirection start with a stolen mailbox login.
- Anyone handling regulated data. Think patient records in a dental or medical practice, client files in a law firm, or tax data in an accounting office.
- Everyone else. Roll out in waves once the first groups are stable.
The same logic applies to guests and outside collaborators. If you share Teams or SharePoint with outsiders, close those MFA gaps as part of the plan.
A rollout plan for a small business
Step 1: Take inventory
List every cloud app, VPN, remote access tool and vendor portal that holds a login. Mark which support passkeys or security keys. Anything that only supports SMS or app codes stays on your "compensate" list, with strong passwords and monitoring.
Step 2: Pick your authenticators
Most small offices land on a mix:
- Passkeys in Microsoft Authenticator for staff with a supported modern phone. No extra hardware to buy.
- Windows Hello for Business on company-managed Windows laptops, using the device's PIN or biometrics.
- FIDO2 security keys for administrators, shared workstations and anyone without a suitable phone. Buy at least two per admin.
Step 3: Plan recovery before you enforce
This is the step most rollouts skip. Decide what happens when someone loses a phone or key. A documented process, a spare key stored securely, and a Temporary Access Pass issued after identity verification will keep a lost device from becoming a lockout. Keep one tested emergency admin account excluded from the policy, with a long unique password stored offline and monitored sign-ins.
Step 4: Pilot, then communicate
Microsoft recommends running an internal campaign before you enforce passkey use and enabling a Temporary Access Pass or other methods to help users register, per its passkey deployment guidance. In practice: pick five to ten users, including one skeptic, run for two weeks, and write down every question they ask. Those questions become your staff handout.
Step 5: Enforce with Conditional Access
Create a policy that requires the phishing-resistant authentication strength for your admin group first. Test it in report-only mode if your licensing allows, then switch it on. Widen the scope group by group.
Step 6: Remove the weaker paths
This is where many organizations stop too early. If SMS and push remain available as fallback methods for the same account, an attacker can simply ask for the weaker option. Once a user is registered and working with a strong method, retire the weaker ones for that account.
What phishing-resistant MFA does not cover
It closes one big door, not all of them. IBM notes that infostealer malware on a compromised device can still harvest session tokens, and that endpoint detection and response can catch threats outside MFA's scope. If an attacker steals an active session from an infected laptop, the strong sign-in already happened.
So the controls around it matter. CISA, NSA, FBI and MS-ISAC recommend that small and mid-sized businesses pair MFA with strong password policies, DNS filtering or firewall denylists, and antivirus. Our firewall best-practice checklist covers the network side. If you want a wider look at your cloud environment beyond sign-in, a cloud security assessment shows how findings turn into fixes.
Backups belong in the same conversation. If an account is ever compromised, a tested, separate backup is how you recover. See our backup and recovery service for how we approach that.
How we help Oklahoma small businesses get there
Most owners we talk to do not want a lecture on FIDO2. They want to know that the person who can wire money or open patient files cannot be fooled by a fake login page. That is what we set up and manage for small businesses in Norman, Moore and Oklahoma City: Microsoft 365 sign-in policies, passkey and security key rollout, recovery procedures, and 24/7 monitoring behind it, explained in plain language and with no long-term contract.
If you are not sure where you stand, start with our 10-minute readiness audit, which is free. To have us handle the rollout, see our Cybersecurity and Microsoft 365 Support services.
Common rollout mistakes
- Enforcing before registering. Users hit a wall and open tickets. Register first, enforce second.
- Applying an All resources policy too early. It can create the registration loop described above.
- One key per admin. Lose it and you lose access. Always register a backup.
- Leaving weak methods enabled. The attacker will choose the weakest path available.
- Forgetting old devices. Phones below the required operating system versions cannot use Authenticator passkeys, so give those users a security key.
For a broader view of what else commonly goes wrong, read our list of IT mistakes small businesses make and the IT services checklist for small business.
FAQ
Is Microsoft Authenticator phishing-resistant?
Only when you use passkeys in Authenticator. Microsoft Entra ID lists those as phishing-resistant. Number-matching prompts, push approvals and one-time codes from the app can still be phished.
How do I make MFA phishing-resistant?
Switch the sign-in method to passkeys, FIDO2 security keys, Windows Hello for Business or certificate-based authentication. Then require that strength through Conditional Access and remove SMS and push as fallbacks for those accounts. Start with administrators.
What is the difference between passwordless MFA and phishing-resistant MFA?
Passwordless means no password is typed. Phishing-resistant means the method cannot be relayed through a fake site. In Microsoft's built-in strengths, Authenticator phone sign-in counts as passwordless but not phishing-resistant.
Does Office 365 have phishing-resistant MFA?
Yes. Microsoft 365 uses Microsoft Entra ID, which supports passkeys in Authenticator, FIDO2 security keys, Windows Hello for Business and certificate-based authentication. An administrator enables them in the Entra admin center and can require them with Conditional Access.
Is phishing-resistant MFA worth it for a small business?
For administrator accounts and anyone with access to sensitive data, yes. NIST's small business guidance points to exactly those accounts as the priority. You can phase it in group by group rather than all at once.
Sources
- Implementing Phishing-Resistant MFA (CISA)
- NIST update on multi-factor authentication and SP 800-63
- What is Phishing Resistant MFA and How Does It Work? (IBM)
- Phishing-Resistant Authenticator Playbook (IDManagement.gov)
- Conditional Access authentication strengths (Microsoft Learn)
- Microsoft Entra authentication overview (Microsoft Learn)
- Enable and support passkeys in Authenticator (Microsoft Learn)
- Passkey self-registration question (Microsoft Q&A)
- Multi-Factor Authentication (NIST Small Business Cybersecurity)
- Phishing Guidance: Stopping the Attack Cycle at Phase One (CISA)
- Cloud security assessment